Agents that fix security findings
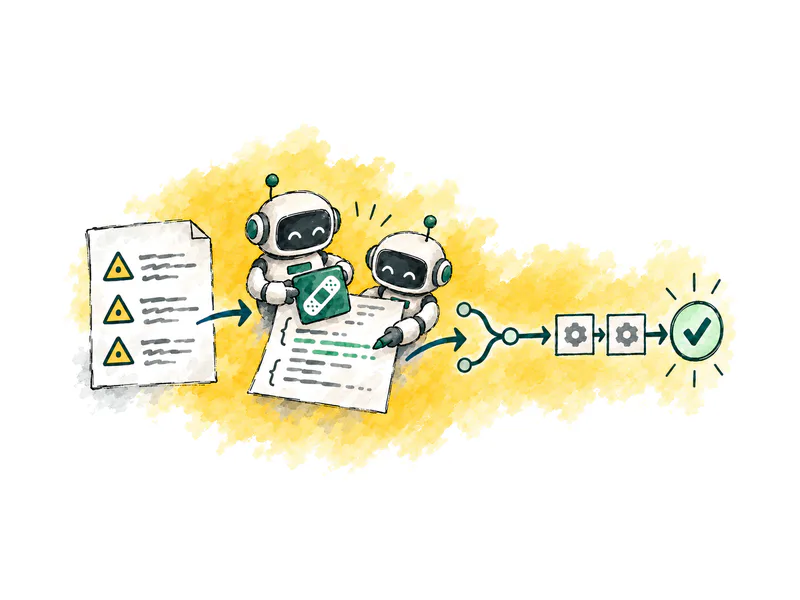
What it is. Security scanners find problems faster than teams can fix them, and most of the fixes are repetitive. On a cross-team initiative, we built agents that take a static-analysis finding all the way to a merge request and through the project’s pipeline. They now open merge requests for teams across the organization, and another team built them into its own agent platform.
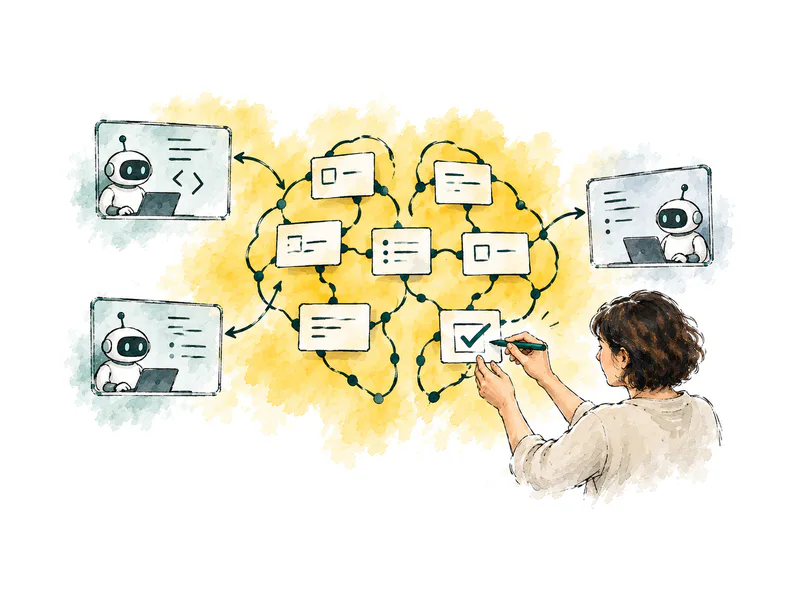
My part. I was one of the lead engineers. I built the remediation agents and shaped how they stay safe and how their work gets checked. Every finding is sorted first: the agent may fix it, a developer gets guidance for the fix, or it’s outside what the agent may touch. The security owners carry the risk, so we agreed with them what the agent may do on its own. The model has no credentials and can’t push code; plain, deterministic code does those steps. Tool checks and a separate verification agent look at every fix, and a failed check guides the next attempt. Then a second loop works on whatever breaks in the project’s own CI.
“The challenge was not simply to have AI generate a fix, but to build a workflow that engineering and security could trust.”
Stack: AI agents, static analysis, merge requests, CI pipelines.